Key takeaways
- Patchright is a patched Chromium build driven by Playwright's own API, not a separate library to learn.
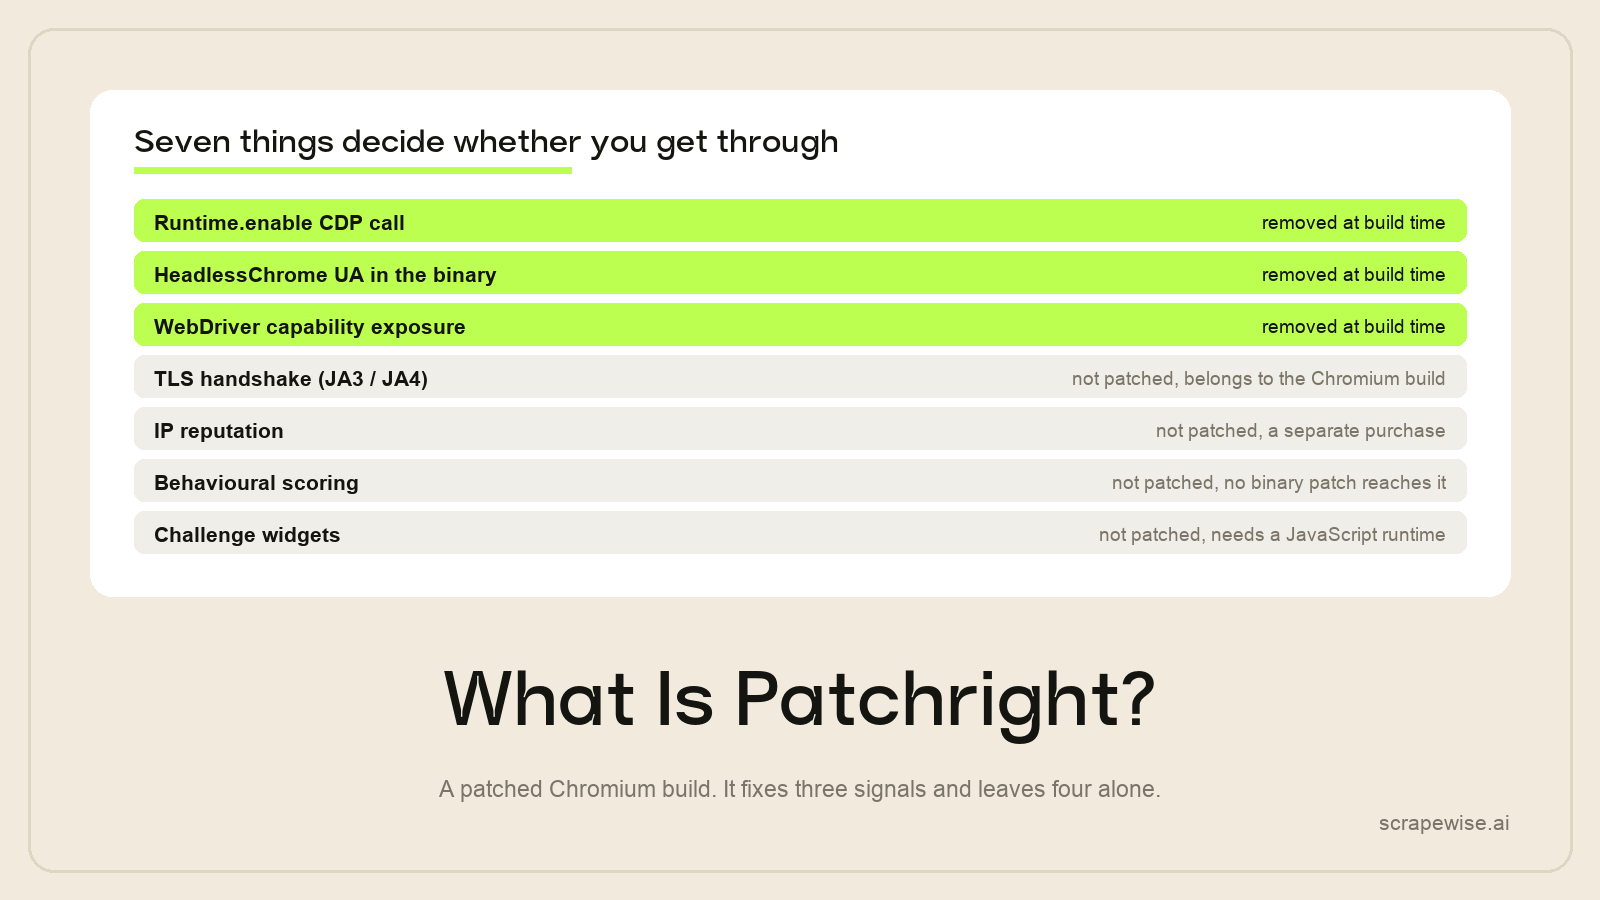
- It removes three detection signals at build time: the Runtime.enable CDP call, the HeadlessChrome UA string compiled into the binary, and WebDriver capability exposure.
- Install is pip install patchright or npm i patchright, then a one-line import change. There is no Go, Java or .NET port.
- Chromium only. A suite running Firefox or WebKit keeps vanilla Playwright for those legs.
- It fixes fingerprint signals, not behavioural ones, and it does not give you proxies.
Patchright is Playwright with the headless tells patched out of the Chromium build. Same API, same selectors, same page.goto(). The difference is that the browser it launches was compiled without three signals that vanilla Playwright announces about itself, and that anti-bot vendors check for.
If you arrived here from a patchright search wanting to know whether it is a new automation framework you need to learn: it is not. It is a drop-in package. The interesting questions are what it patches, what it leaves alone, and whether that is enough for your target.
Patchright in One Table
| Answer | |
|---|---|
| What it is | A patched Chromium build plus a thin Playwright-compatible driver |
| Language support | Python and Node.js. No Go, Java, .NET or Rust port |
| Browser support | Chromium only |
| API | Identical to Playwright, drop-in |
| Memory per instance | ~200MB, no overhead over standard Chromium |
| Maintained by | A small independent team (Kaliiiiiiiiii-Vinyzu) |
| Licence | Open source, free |
| Fixes fingerprint signals | Yes |
| Fixes behavioural signals | No |
| Provides proxies | No |
Installing Patchright
Python:
pip install patchright
patchright install chromium
Node.js:
npm i patchright
npx patchright install chromium
Then change the import. Python:
from patchright.sync_api import sync_playwright

with sync_playwright() as p:
    browser = p.chromium.launch(headless=True)
    page = browser.new_page()
    page.goto("https://example.com")
    print(page.title())
    browser.close()
Node.js:
const { chromium } = require('patchright')

const browser = await chromium.launch({ headless: true })
const page = await browser.newPage()
await page.goto('https://example.com')
console.log(await page.title())
await browser.close()
That is the whole migration. Your selectors, page objects, waits and context handling carry over unchanged, because they are Playwright's and Playwright has not changed. Extraction is ordinary Playwright too — nothing about the patched build changes how you read a page:
from patchright.sync_api import sync_playwright

with sync_playwright() as p:
    browser = p.chromium.launch(headless=True)
    page = browser.new_page()
    page.goto("https://example-retailer.de/category/laptops",
              wait_until="domcontentloaded")
    page.wait_for_selector("[data-product-card]")

    for card in page.query_selector_all("[data-product-card]"):
        print({
            "name":  card.query_selector("h3").inner_text().strip(),
            "price": card.query_selector("[data-price]").inner_text().strip(),
            "url":   card.query_selector("a").get_attribute("href"),
        })
    browser.close()
One habit worth keeping: wait_for_selector on a real content element, not a fixed sleep. A patched browser that still waits exactly 3,000ms on every page has handed back a behavioural signal it did not need to.
Two install-time details that cost people an afternoon. The patched Chromium is downloaded and cached separately from Playwright's own browser cache, so a CI image that already pins a Playwright browser now pulls a second build. And if both packages are installed in the same environment, an import left pointing at playwright silently gives you the unpatched browser — the run succeeds, the block rate does not change, and nothing in the logs tells you why.
What Gets Patched, and Why Build Time Matters
Vanilla Playwright is not trying to hide. It is a testing tool, and it announces itself in ways that cost nothing in CI and everything in production scraping.
1. The Runtime.enable CDP leak. Playwright calls Runtime.enable over the Chrome DevTools Protocol to set up its execution-context bookkeeping. That call is observable from inside the page, and Cloudflare's current detection watches for it specifically. Patchright avoids the call and resolves execution contexts differently. This is the patch that matters most in 2026 and the reason Patchright clears targets that playwright-extra does not.
2. The HeadlessChrome user-agent string inside the binary. Not the runtime navigator.userAgent you can override with a launch argument — the string compiled into the Chromium build, which surfaces in places a JavaScript override never reaches.
3. WebDriver capability exposure. navigator.webdriver and its supporting plumbing, removed at the C++ level rather than deleted from the page context after load.
The structural reason this works: the patches land before the browser process starts, not in the page. A JavaScript-injection approach has to redefine properties after load, and redefinition is itself detectable — an Object.defineProperty guard can spot a property whose descriptor was rewritten. There is nothing to spot when the property was never compiled in.
Two consequences follow from the same fact: no JS injection cost at page load, and a TLS fingerprint closer to a real Chrome session.
The Four Limits That Decide Whether It Helps
This is the section most patchright write-ups skip, and it is the one that decides whether the package solves your problem.
It does not address behavioural scoring. Every modern WAF scores mouse-movement paths, scroll velocity, dwell time before the first click, keystroke cadence and the timing distribution of requests. A patched browser that loads a page, reads the DOM in 400ms and leaves has a signature no binary patch touches. Against Akamai Bot Manager v4 and PerimeterX/HUMAN this is usually what catches Patchright sessions.
It does not give you proxies. A clean fingerprint from a datacentre IP that has already been flagged is refused at the edge before anything in the browser is evaluated. In our April 2026 tests Patchright reached 74% against Akamai v4 on residential proxies; the IP layer is doing a large share of that work.
It does not cover Firefox or WebKit. Patchright is a Chromium patch. Cross-browser suites keep vanilla Playwright for the other two engines, which means two browser caches and two code paths.
It does not exist outside Python and Node. The patchright go, patchright java and patchright .NET searches have no answer: there is no port. Playwright itself ships in those languages, Patchright does not. On a Go stack the realistic options are driving a patched Chromium over raw CDP yourself, or moving the fetch layer out of the browser entirely — see TLS fingerprint impersonation with curl_cffi.
Does Patchright Bypass Cloudflare?
On Cloudflare's free BotFight tier, consistently. On Cloudflare Enterprise and Turnstile, results vary by target — which is an honest "sometimes", not a hedge.
The reason it does better than playwright-extra is the Runtime.enable patch, because that is the signal Cloudflare's current detection looks for. The reason it still fails on Enterprise is that Enterprise also runs behavioural scoring, and no binary patch reaches it.
Worth being concrete about the common failure sequence, because it is nearly always the same:
- Vanilla Playwright is blocked immediately.
- Patchright passes. The problem looks solved.
- Volume goes up. Rate-limiting starts.
- Residential proxies are added. Pass rates recover.
- Behavioural scoring catches the request timing.
- You are now writing a mouse-movement simulator.
Step 6 is where most teams discover that stealth was never a library choice.
How Patchright Compares to Camoufox, noDriver and playwright-extra
| Tool | Best for | Strengths | Limitations |
|---|---|---|---|
| Playwright | Tests, unprotected targets | Reference implementation, all three engines, Microsoft-maintained | Announces itself; blocked by any real WAF |
| Patchright | A Python or Node scraper that Cloudflare is blocking | One-line migration, no runtime overhead, free | Chromium only, no behavioural handling, no proxies, small maintainer team |
| Camoufox | High-value, low-frequency protected targets | Firefox fork patched at C++ level, 0% headless detection on standard tests | Averages 42.49s to clear a Cloudflare challenge; wrong for a daily catalogue crawl |
| noDriver | Lightweight crawls, no Chromium overhead | ~80–120MB, drives Chrome over CDP with no Playwright | No behavioural handling, blocked quickly by anything scoring it |
| playwright-extra | Nothing new | Historical interest | Effectively unmaintained, blocked on Cloudflare Enterprise. Do not start new work on it |
| ScrapeWise | Teams that want the rows, not the stack | Managed browsers, proxies and challenge handling; pay per delivered page | Not a library you control — you cannot script arbitrary in-page behaviour, and it is a paid service |
The full measured matrix across all five open-source options is in the Playwright stealth benchmark. For the head-to-head on the specific signals, see Patchright vs Playwright, and for the Firefox comparison, Camoufox vs Patchright.
Patchright by Anti-Bot System
| System | Patchright result | Better choice if it fails |
|---|---|---|
| No WAF | Passes — Patchright buys you nothing over Playwright | Playwright |
| Cloudflare BotFight | Passes | — |
| Cloudflare Enterprise / Turnstile | Variable | Camoufox |
| Akamai Bot Manager v4 | 74% on residential proxies | curl_cffi, 87% — skip the browser |
| DataDome | Variable | Browser is mandatory here |
| PerimeterX / HUMAN | Variable | Every approach hits a ceiling |
The Akamai row is the counter-intuitive one and worth internalising: on Akamai, TLS fingerprinting is the primary signal, so a correct HTTP client beats a patched browser outright and costs about a quarter as much to run. The full argument, including when to keep the browser anyway, is in Playwright vs Akamai Bot Manager.
Where the Patching Cycle Stops Paying Off
Stealth tools decay. Each anti-bot vendor ships detection updates, each update needs a corresponding patch, and the gap between the two is downtime on whichever data source you depend on. Akamai alone pushes sensor-script changes roughly monthly, and each one can drop a pass rate by 15–30 points overnight.
That maintenance cycle does not appear in any install command, and it is the real cost of a self-hosted stealth stack.
If what you need is competitor prices, stock levels and product data arriving in your systems rather than a stealth stack to keep alive, the Patchright question is the wrong one to be answering. ScrapeWise runs the browsers, the proxies and the challenge handling and delivers structured rows. No plan and no compute units: a balance you top up, and a published charge per delivered page — EUR 0.15 per 1,000 for plain requests, EUR 0.75 with rendering, EUR 1.50 through the residential tier and EUR 3.75 for render plus residential. New accounts get 5 free requests and the balance never expires.
You can also call ready-made scraping API endpoints directly, or see how this feeds competitor price tracking.
So Should You Use Patchright?
- Yes — you have a Python or Node scraper that Cloudflare is blocking. It is the cheapest upgrade available and costs you one import line.
- No — you are writing tests, or your target has no WAF. Use Playwright.
- No — you are on Go, Java or .NET. There is no port; fix the TLS layer instead.
- Not enough — you are on Akamai. Drop the browser and get the handshake right.
- Not the question — you want delivered rows on a schedule and would rather not run a stealth stack at all.
Paste any URL — ScrapeWise handles the anti-bot
Managed infrastructure that adapts when sites change. No proxies, no code, no per-request fees.
Not ready to sign up? See 12 real Amazon rows, 972 columns →
97% accuracy on Amazon benchmarks · no credit card · book a 15-min call →